

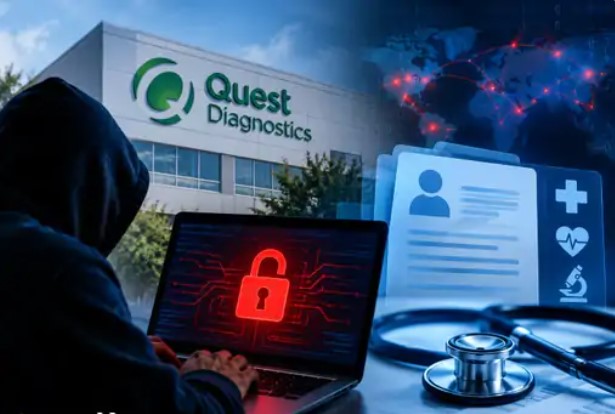
CNN Central News & Network-ITDC India Epress/ITDC News Bhopal: New Delhi/Washington (Reuters). Quest Diagnostics, among the major medical laboratory companies in the United States, has reported a cybersecurity breach in one of its digital systems. According to the company, unauthorised access was gained to its Quanum Lab Services Manager platform, affecting some patient records. The system helps healthcare providers order lab tests and receive their reports.
The matter, which came to light on October 22, 2026, is being investigated. The company has involved federal law enforcement agencies and outside cybersecurity experts in the probe. It is not yet clear how many patients’ data was affected or what information was included.
Questions over the security of patients’ personal information Medical laboratories use sensitive data such as patients’ names, contact details, test-related information and health records. If such information falls into the hands of unauthorised individuals, it can be misused for identity theft, fraud or fake medical claims. However, in the Quest Diagnostics case, it has not yet been confirmed that data from all these categories was leaked.
The company is assessing which records were accessed and the actual scope of the incident. According to initial information, precautionary steps have been taken regarding the affected system. There has been no confirmation of a broad impact on the company’s core services.
Cyberattacks rising against healthcare sector The healthcare sector remains a target for cybercriminals. According to a report published in July 2026 by cybersecurity research organisation Comparitech, 410 ransomware attacks were recorded against healthcare organisations worldwide in the first half of 2026, compared with 360 in the second half of 2025. Of these, 225 incidents were linked to the United States. The report included incidents targeting hospitals and clinics, as well as medical device manufacturers, health technology companies and medical billing services.
In its third-quarter report released in October, Comparitech cited 306 ransomware incidents and claims related to the healthcare sector worldwide between July and September 2026. Of these, 185 cases were linked to the United States. According to the report, many of the claims were unverified and therefore cannot be considered confirmed cyberattacks in all cases.
Strong systems needed for data security According to experts, medical institutions should adopt measures such as multi-factor authentication, data encryption, regular security audits and continuous monitoring of suspicious activity to protect patient records. Training employees to identify phishing emails and suspicious links is also necessary.
The latest Quest Diagnostics case shows that as healthcare services become increasingly digital, the security of patients’ personal information has become equally important. Only after the investigation is completed will it be clear how many people were affected in this incident and how great the risk of potential misuse of data is.
Hashtags: #WorldInternational #Bhopal #USMedicalLab #Cyberattack #PatientData #QuestDiagnostics #US #Medical #Lab #Patients